Do you need a control plane if your agents already run in a sandbox?

People ask this in almost every conversation about ACP: “We already run our agents in Docker, a micro-VM, or the harness’s sandbox. Isn’t this redundant?”
No. They do different jobs. Keep the sandbox.
What a sandbox covers
A sandbox is a wall around where code runs. Docker, gVisor, a micro-VM like pi’s Gondolin, a cloud execution environment, or the sandbox in Claude Code or Codex all limit the files, processes and network on one host. If the agent runs a malicious binary, or a poisoned dependency makes arbitrary system calls, or the agent runs rm -rf on its working directory, the damage stops at the wall.
ACP does not replace that. It checks tool calls. It is not a system-call filter, so it can’t help if a process is compromised underneath the tool call.
What a sandbox can’t see
A sandbox has no opinion about actions taken with valid credentials through allowed channels. That is most of what an agent does all day.
- An agent merges the wrong PR using your GitHub token, over HTTPS, through an egress rule you allowed. The sandbox let it through because that is what you told it to do.
- In the Amazon Q incident we recreated, the injected instruction told the agent to delete cloud resources with the developer’s own permissions. Put that agent in a container and the local wipe stays contained. The
gclouddeletions still go through if the credentials are mounted and the API calls are well formed. - A run that burns $50 in a re-read loop never touches a file it shouldn’t. A sandbox doesn’t meter tokens.
- When something goes wrong, a sandbox has no record of which call did it, under whose identity, or why it was allowed. It can tell you the process exited.
Sandbox settings also drift. When we read the source of fifteen harnesses and frameworks in July 2026, CrewAI’s code interpreter fell back to in-process exec() when Docker wasn’t there. The path that was supposed to be sandboxed failed open. If the sandbox is your only layer, you won’t see it go missing.
Who decides what
The sandbox limits the machine the agent is on. ACP decides each tool call the agent makes, and your repos, cloud accounts and model bill sit behind those calls. One is a wall. The other is a check at each door, with a log of every answer.
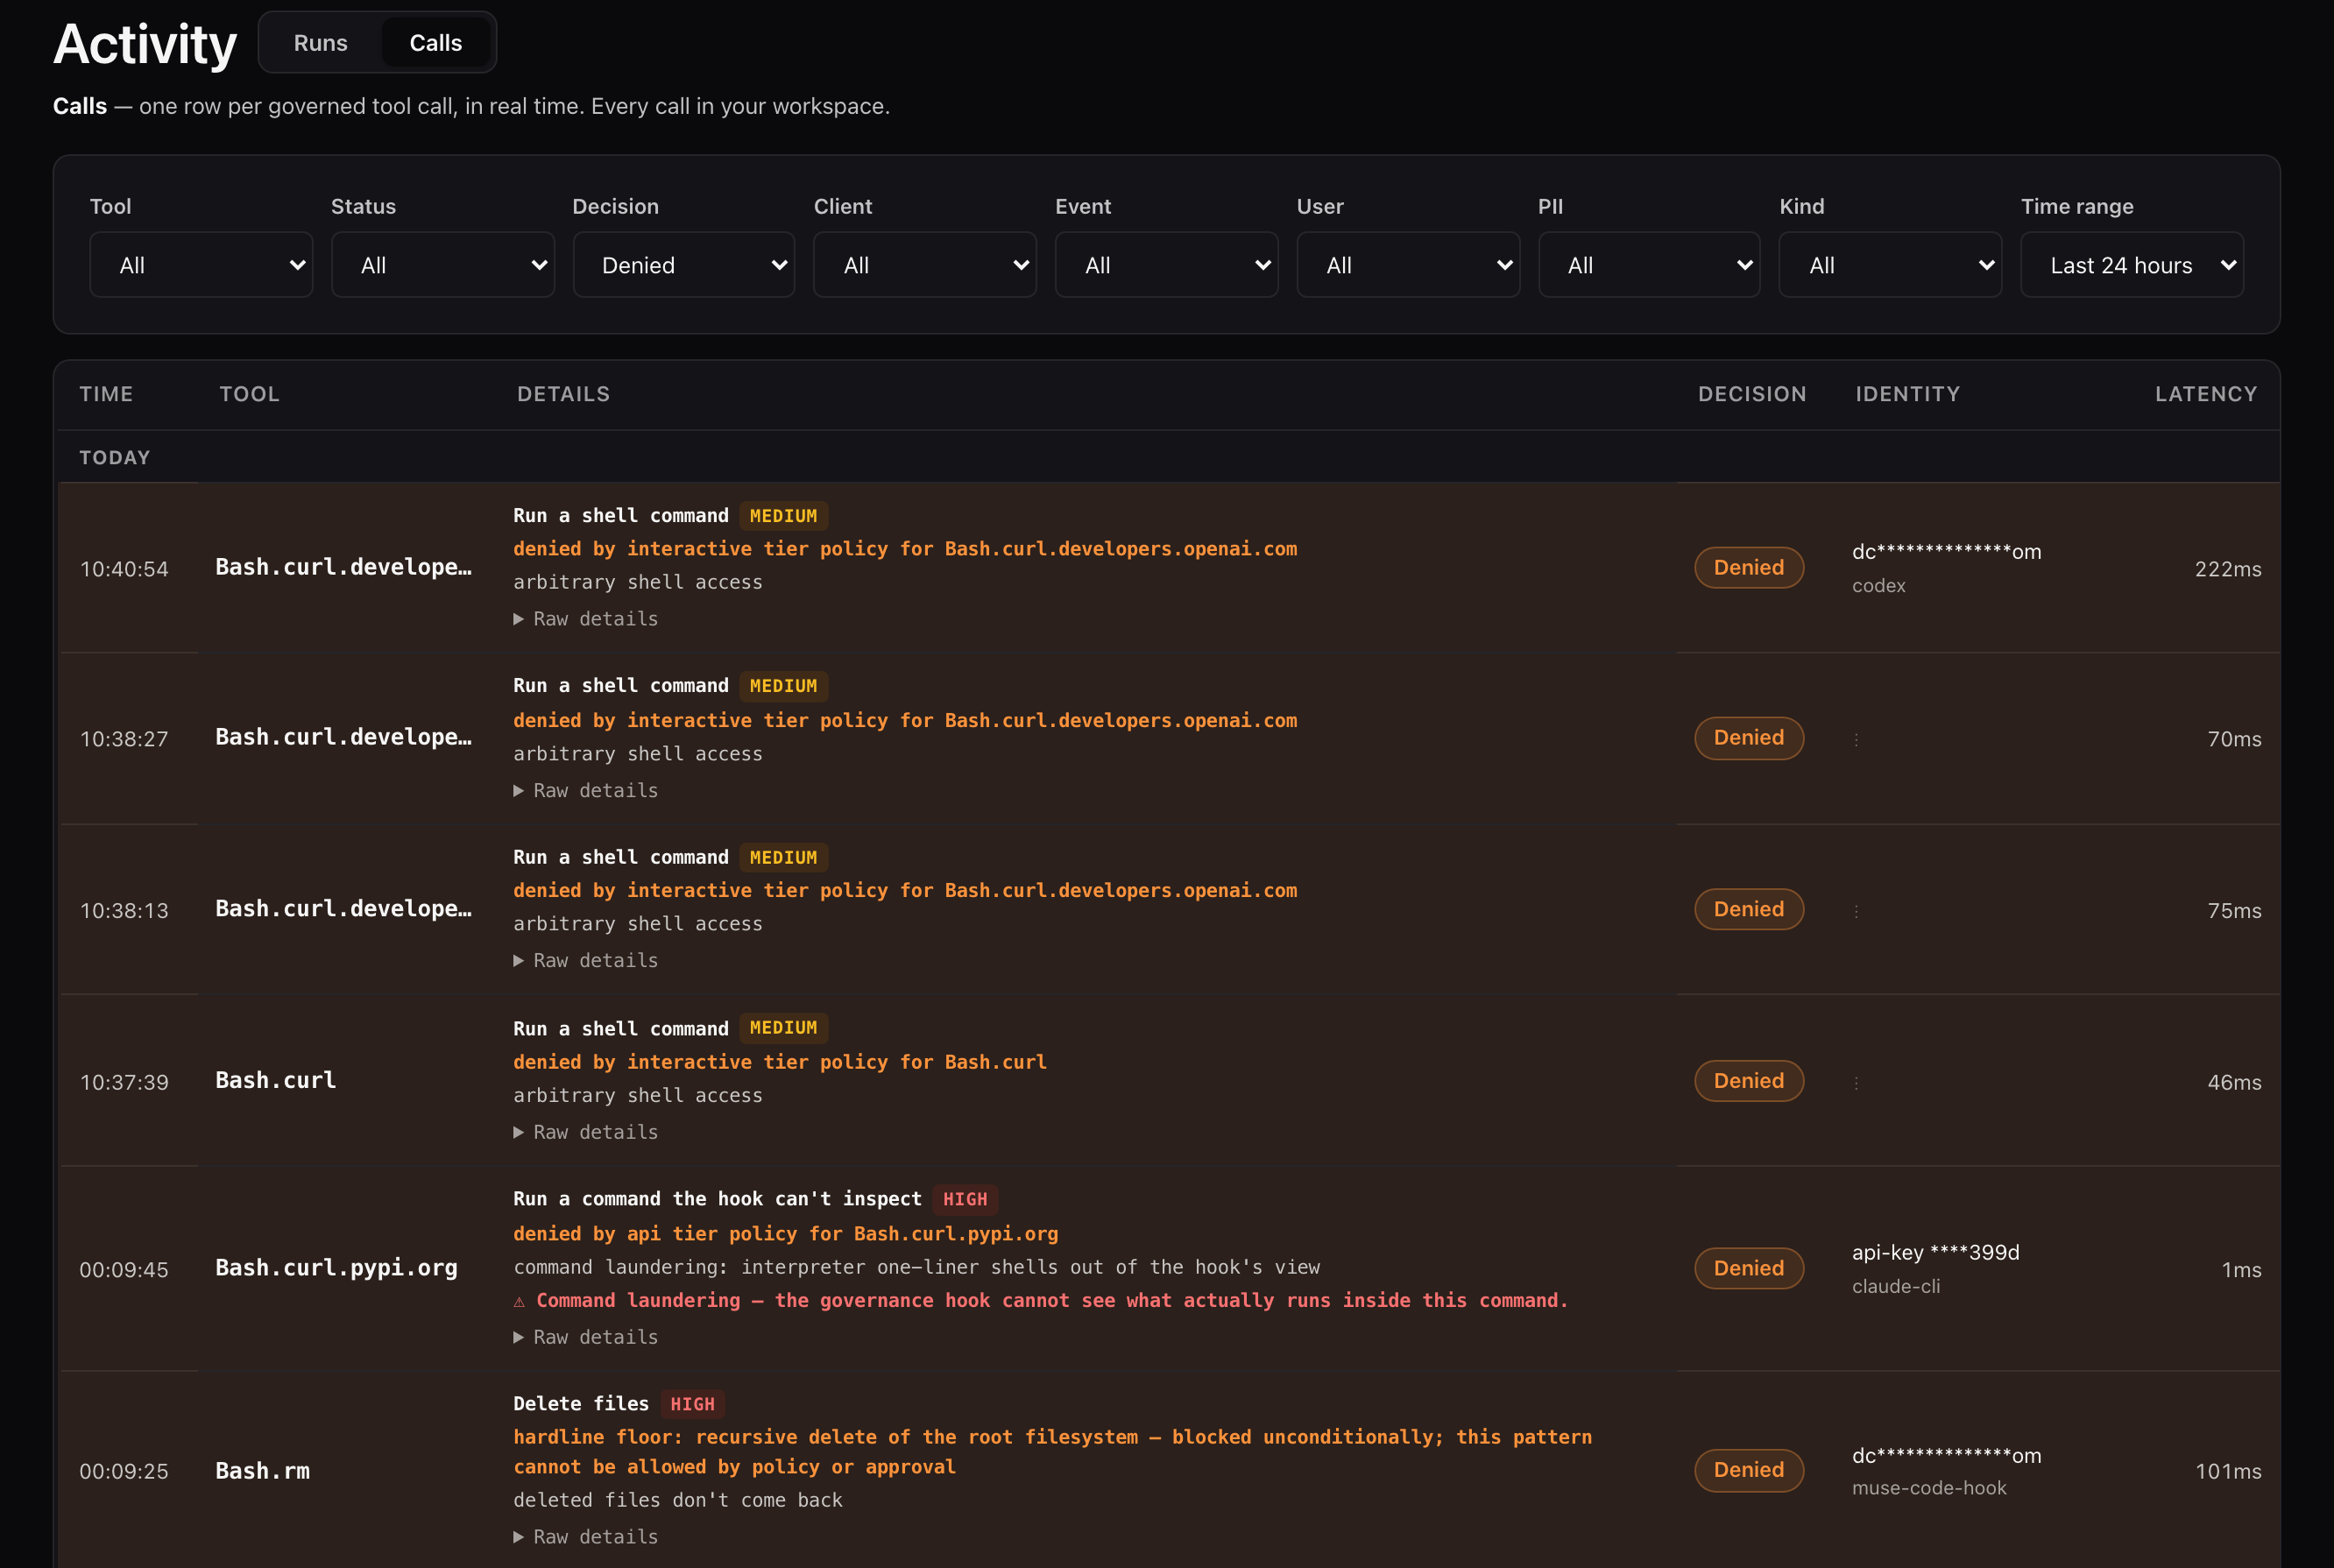
One workspace's denied calls in the activity log (Aug 18, 2026). A sandbox would not have stopped any of them. The Bash.rm row is the safety floor: a recursive delete of the root filesystem is always blocked, in every mode, and no approval reaches it.
How they fit together
Here is the order, from the model outward. The model proposes an action. The harness turns it into a tool call. ACP’s hook checks the call and answers allow, ask or deny. If it’s allowed, the sandbox contains how it runs. Whatever the call legitimately reaches outside the sandbox is limited only by that earlier decision.
The two don’t get in each other’s way. The hook is an ordinary process, so it can run inside the container. In a connected workspace it also needs to reach the ACP gateway over the network, so your egress rules have to allow that. pi’s docs tell you to containerize if you want a boundary. Our pi extension works alongside that and checks calls before they run.
One limit to know about: ACP runs as a hook on the client. If something switches hooks off, it stops checking. disableAllHooks does that in Claude Code, and so does Antigravity’s --dangerously-skip-permissions. A sandbox still holds when that happens.
Keep the sandbox, and tighten it if you can. Then add a check on the calls that go out through it.
Running coding agents? ACP records each tool call its hook sees and makes the dangerous shell commands (a force-push, destructive SQL, curl | sh) wait for you. One command, free up to 5 agents:
curl -fsSL https://agenticcontrolplane.com/install.sh | bashirm https://agenticcontrolplane.com/install.ps1 | iex