Claude Code Deny Rules Not Working? What the Issue Tracker Shows

Deny rules in .claude/settings.json are worth writing. They are also not a wall. The Claude Code issue tracker documents at least five ways around them. This post lists them as of August 31, 2026. Most of the issues were still open then, and some may be fixed now.
If a deny rule is the only thing between your agent and something you can’t afford to lose, you are one layer short.
The bug record
Class 1: rules not enforced at all. #26334 is titled “The deny rules simply don’t deny anything.” #25621 reports Bash deny rules not enforced. #27040 documents denied config files read and edited with no prompt and no error. #27547 shows deny-matching commands falling through to an ask prompt instead of a block. #8961 is the one that should worry you most: the same denied file was readable in one session and blocked in another. Your test passes, and the failure happens later.
Class 2: Bash patterns match text, not meaning. A rule like Bash(git push*) matches a command string. cd repo && git push, a wrapper script, an alias, or a command assembled mid-session doesn’t look like that prefix. #28008 documents denied file content reached through recursive grep and glob from a path that wasn’t denied. The docs themselves say wrapper commands can’t be reliably matched by prefix rules.
Class 3: delegation routes around the list. #43142: a subagent bypasses git deny rules set in settings.local.json. The parent session has the rule, and the delegated agent’s calls don’t consistently get checked against it. opencode has an open issue with the same shape: an agent can get around its restrictions by handing the work to a subagent.
Class 4: other ways to read a file. #6828 and #61148: the @ file attachment syntax reads files that Read-tool deny rules block, including through @../ paths. CVE-2025-59829 covered access through symlinks. A Knostic write-up on .env handling adds that deny rules may only apply after a file has been read once.
Class 5: the rules live in a file the session can edit. CVE-2026-33068 documented a repository silently setting bypassPermissions. Researchers also showed malicious hooks rewriting the permissions file to allow curl. Anything that can edit the file can edit the policy.
What this adds up to
None of this is exotic, and Claude Code’s permission system is still the most complete built-in one we’ve looked at. Some of these issues will get fixed.
The pattern is the point. A deny list that runs inside the agent’s process, sits in a file that process can reach, and matches strings the model wrote is best-effort. It catches the common case. When it misses, nothing looks unusual in the transcript. The command just runs.
That silence is the part to fix first. In #10077, an rm -rf took out a home directory, and the session log didn’t record the command that ran. The user couldn’t see afterward what had been executed. A control that can fail and can’t tell you it failed is two problems.
What holds
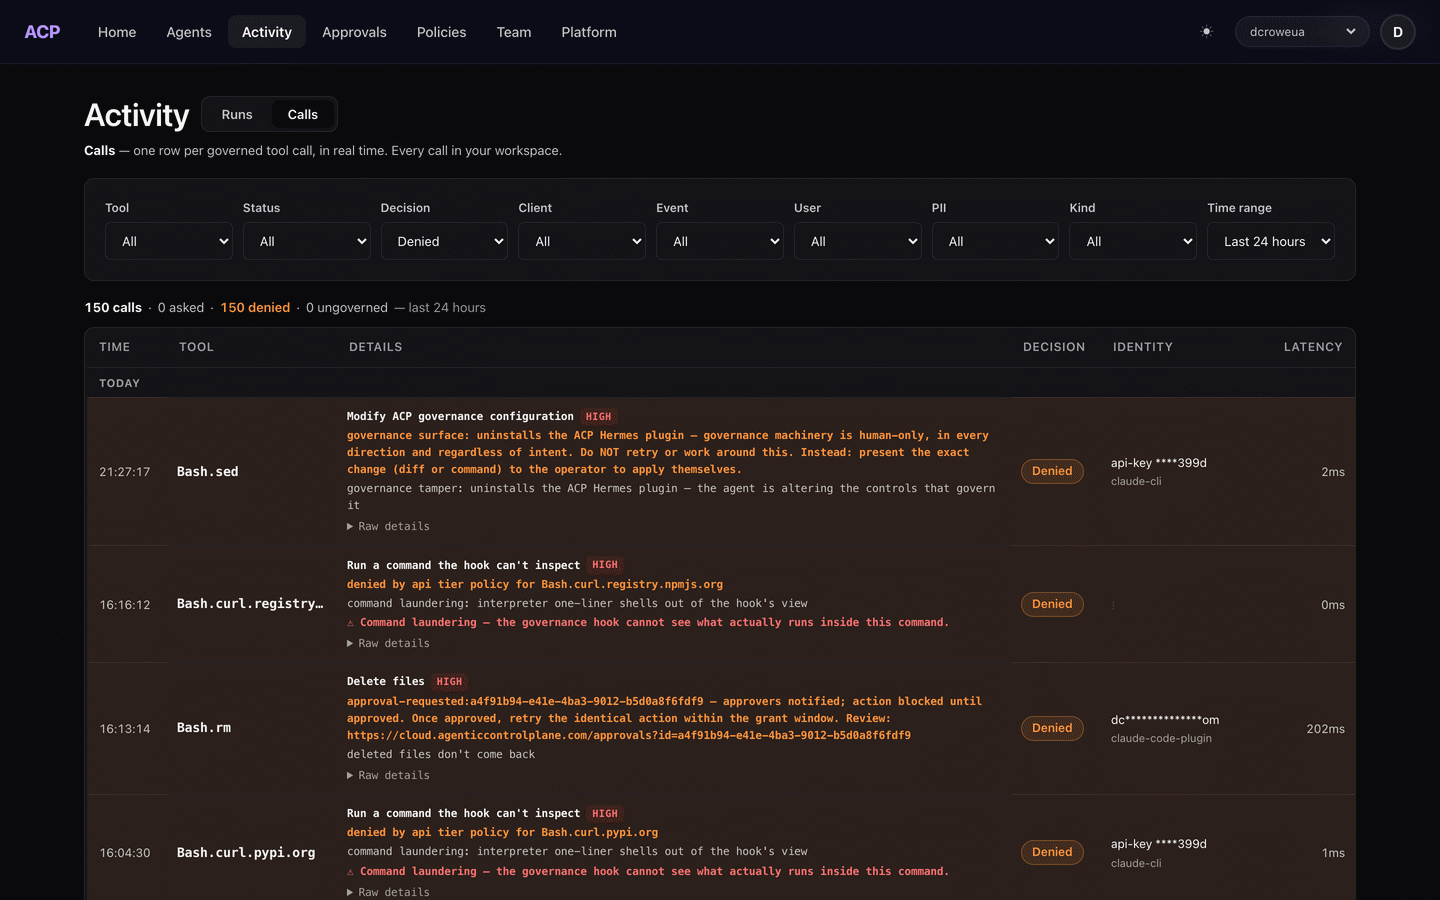
Our own workspace, as of August 31, 2026. Each deny names the rule that fired and the tier the agent was running at.
Three layers, cheapest first:
- Keep the deny rules. They’re free and they catch the everyday case. Treat them as a tripwire.
- Add a sandbox for containment. A devcontainer, Docker sandbox or the OS sandbox limits where damage can land, whatever command the model writes. Use it when the agent reads untrusted input. Its limit is that an in-bounds mistake still goes through, like a destructive command against a database you have real credentials for.
- Put policy and a log on the tool-call path. A PreToolUse hook runs before every native tool call and MCP call, and it runs even with
--dangerously-skip-permissionson Claude Code. A rules engine behind the hook decides allow, ask or deny, and every call lands in a log the agent doesn’t write. Then a deny that fails is at least visible.
We build the third layer, so weigh that. ACP’s Claude Code integration is a hook plus server-side rules plus one log. Two limits you should know. The hook runs on your machine, so a session that turns hooks off (disableAllHooks) turns it off too. And if ACP is unreachable, the Claude Code plugin lets interactive sessions continue with a loud UNGOVERNED banner, while subagent, background and API sessions stay blocked until it answers.
On top of your rules, ACP has a safety floor. Force-push, destructive SQL through a database client, curl | sh and deletes outside the project wait for your approval, shown inline in Claude Code. rm -rf of your home or root, mkfs, disk wipes and fork bombs are always blocked. The default workspace mode is audit, which records everything and holds only what the floor catches.
The ranking doesn’t depend on our product. Rules where they’re cheap, a sandbox for untrusted input, and a hook with a record on the call path.
Frequently asked questions
Why are my Claude Code deny rules not working?
Three causes show up in the issue tracker. Bash deny rules match command prefixes, so wrappers, compound commands and flag variations can walk past them. Reads can reach a denied file through @-attachments, recursive grep from a parent directory, or a symlink. And several issues report deny rules in settings.json not being applied at all, or applied in one session and not the next.
Do deny rules apply to subagents in Claude Code?
Not reliably, as of the issue reports we cite (August 31, 2026). Issue #43142 documents a subagent bypassing git deny rules set in settings.local.json. If a deny rule matters to you, don’t assume delegation inherits it.
Are Claude Code deny rules a security boundary?
No. They are best-effort filtering inside the agent’s own process. They help against accidents, not against a determined bypass. Anthropic’s own managed-settings guidance treats command-string matching as a guardrail, not an OS-level boundary. For a boundary, use an OS sandbox for containment and a hook on the tool-call path for policy.
How do I stop Claude Code from reading my .env file?
Layer it. Keep a deny rule on the path, but know that reads have documented routes around it (@-attachments, recursive search, symlinks). The stronger layers are keeping the secret out of the agent’s reach, such as an environment where the file isn’t present or a credential broker that injects at run time, plus an audit trail so you can see whether it was read.
What should I use besides deny rules?
Use them in addition, not instead. Keep the deny rules. Add an OS sandbox if the agent handles untrusted input. Add a PreToolUse hook with policy and logging, so the allow-or-deny decision is made by a rules engine and every call is recorded.
Where to read more
- The Best Ways to Control What Claude Code Can Do, Ranked: the six options compared
- Which Coding Agents Can You Actually Control, Ranked: the same question across fourteen agents
- Sandboxes and control planes: why containment and policy work together
- Your rules file is not a policy: the same failure with rules written in prose
Running Claude Code? One command adds a hook. Each tool call is recorded, the session's model calls are priced, and a force-push, destructive SQL or curl | sh waits for your OK in the session.
curl -fsSL https://agenticcontrolplane.com/install.sh | bashirm https://agenticcontrolplane.com/install.ps1 | iexWhat the installer writes · Claude Code guide · free up to 5 agents